YubiKey 5 FIPS Series
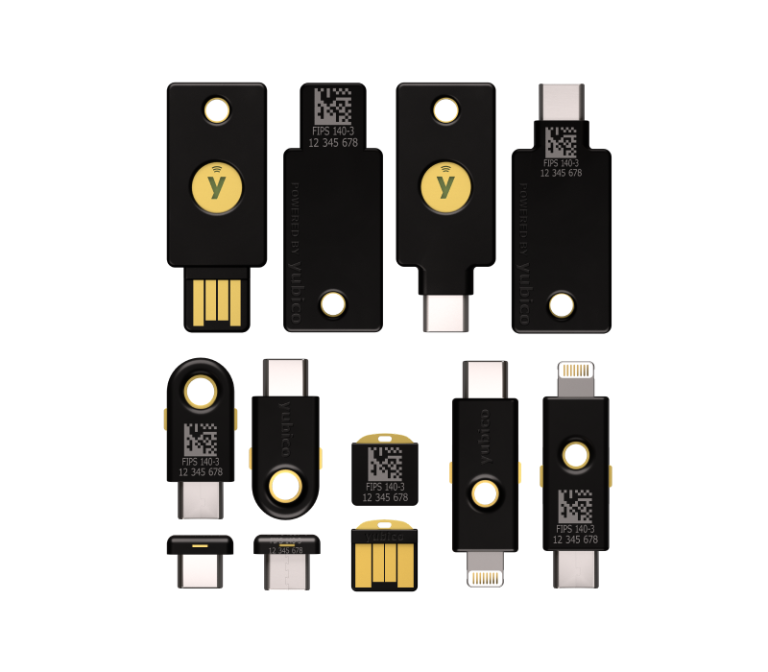
The YubiKey 5 Series with FIPS 140-3 validation, for environments where the certificate matters as much as the cryptography.
Overview
Functionally this is the YubiKey 5 Series, validated to FIPS 140-3 at Overall Level 2 with Physical Security Level 3. It meets Authenticator Assurance Level 3, the highest tier in NIST SP 800-63B, which is the bar most often cited by government bodies, defence suppliers, and regulated financial institutions. Cryptographic support covers RSA 2048, ECC P-256, and ECC P-384.
Specifications
- Protocols
-
- FIDO2 / WebAuthn
- Smart card (PIV/CAC)
- OpenPGP
- OATH-TOTP
- OATH-HOTP
- Challenge-Response
- Form factors
-
- 5 NFC FIPS
- 5C NFC FIPS
- 5Ci FIPS
- 5C FIPS
- 5 Nano FIPS
- 5C Nano FIPS
- Certification
- FIPS 140-3 — Overall Level 2, Physical Security Level 3. NIST SP 800-63B AAL3. RSA 2048, ECC P-256, ECC P-384.
- Durability
- IP68 rated, crush resistant, no batteries, no moving parts
Models
Every key in the series carries identical functionality — the choice is purely about the connector and how the key will be carried.
- YubiKey 5 NFC FIPS
- Slim USB-A with NFC. Keychain-friendly.
- YubiKey 5C NFC FIPS
- Slim USB-C with NFC. Keychain-friendly.
- YubiKey 5Ci FIPS
- Dual connector, USB-C and Lightning, for iOS devices alongside computers.
- YubiKey 5 Nano FIPS
- Slim USB-A sized to sit permanently in the port.
- YubiKey 5C Nano FIPS
- Ultra-slim USB-C for recent Mac, PC and Android hardware.
Features
- FIPS 140-3, Overall Level 2, Physical Security Level 3.
- Multi-protocol support on a single key.
- Crush resistant and water resistant.
- Manufactured in the USA.
Technical specifications
- Supported protocols: FIDO2/WebAuthn, Smart Card (PIV), OATH-TOTP, OATH-HOTP, OpenPGP, Challenge-Response.
- Runs on Microsoft Windows, macOS, Linux and ChromeOS, and in all major browsers.
- PIV smart card compatible, with a minidriver available for Windows.
- PKCS#11 support.
- Cryptographic algorithms: RSA 2048, ECC P-256, ECC P-384.
- A hardware secure element holds the cryptographic keys.
Best for
Government, defence, and regulated sectors where procurement or audit requires a FIPS-validated authenticator rather than an equivalent uncertified one.
Typical uses
AAL3 authentication, government and defence deployments, regulated financial services, and any tender naming FIPS 140-3 as a requirement.