YubiHSM 2
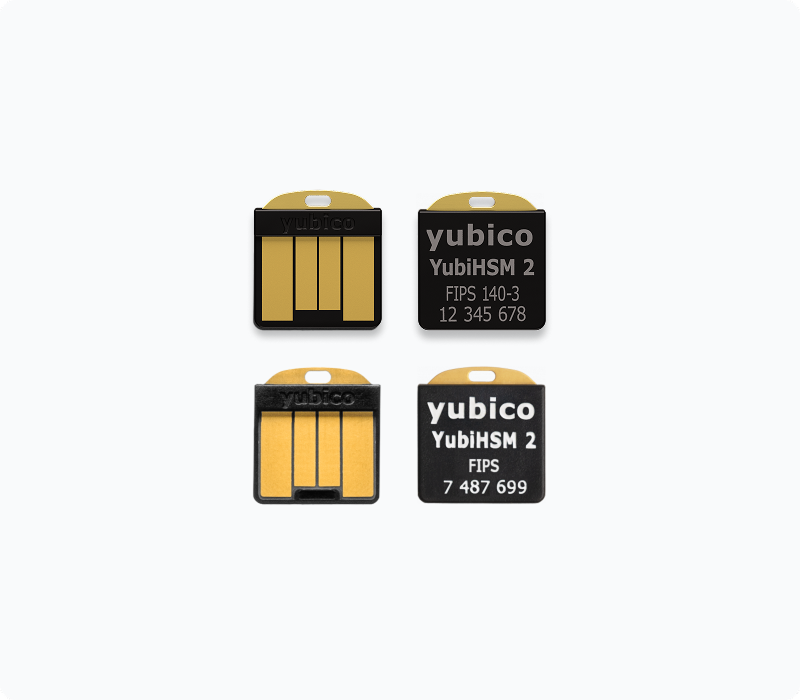
A hardware security module the size of a USB stub. Root-of-trust protection without a rack.
Not a traditional HSM
A nano-format HSM, FIPS 140-3 validated, protecting infrastructure for which a rack-mounted appliance would be disproportionate.
Enhanced protection for cryptographic keys
Secure generation, storage and management of digital keys, performed in hardware.
Rapid integration with hardware-backed security
A comprehensive open-source cryptographic toolbox, with support for PKCS#11.
Simplified deployment for organisations of all sizes
An ultra-portable form factor at a price that suits both long-standing and emerging use cases.
Overview
The YubiHSM 2 generates and stores private keys in hardware so they cannot be extracted, and performs signing and decryption on the device itself. It is the standard answer to "where does our certificate authority root key live?" — traditionally an expensive rack-mounted appliance, here a nano-format device sitting in a server's USB port. Integration is through PKCS#11, the YubiHSM Key Storage Provider for Windows environments, or the native libraries.
Specifications
- Protocols
-
- PKCS#11
- YubiHSM KSP (Windows)
- Native libraries
- Direct USB
- Form factors
-
- Nano
- USB-A
- USB-C
- Durability
- IP68 rated, crush resistant, no batteries, no moving parts
Key protection
- Private keys are generated and held in hardware, so they cannot be copied off the machine or redistributed.
- Remote extraction of a private key is eliminated: signing and decryption happen on the device, and the key never leaves it.
- The YubiHSM 2's own authentication key can itself be stored on a YubiKey, removing one more password from the process.
- Backups use asymmetric wrapping, so a wrapped export exposes no secrets even when it crosses a network to another site.
Integration
- An open-source SDK, so integration work is not gated behind a vendor engagement.
- Exposed through PKCS#11, the industry standard interface, so most existing software can use it without modification.
- Hardware-backed key storage can be built into your own platforms, applications and services.
Deployment
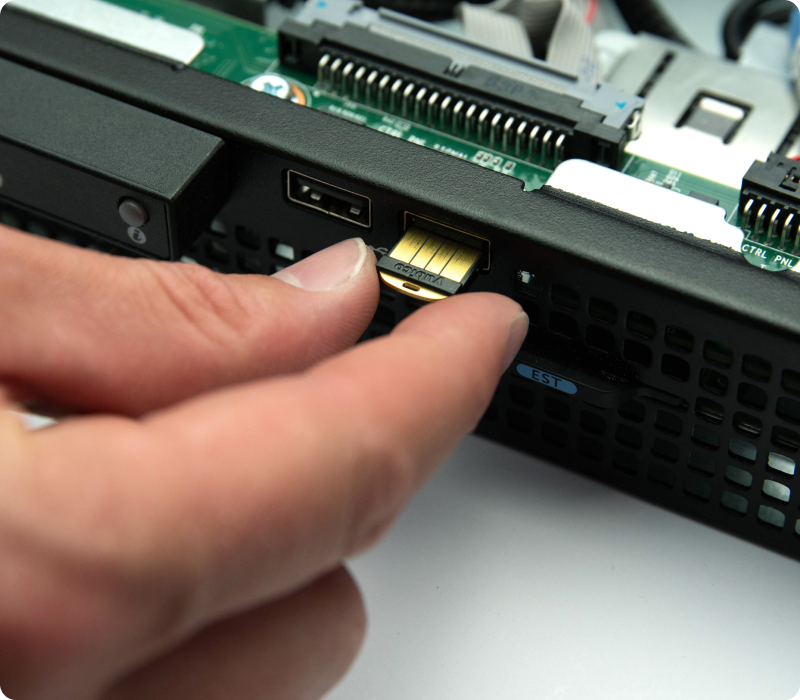
- Fits a front USB slot on a server or workstation — no rack space, no power, no cabling.
- Protects Microsoft Entra ID certificates.
- Used to secure cryptocurrency exchanges, IoT gateways and proxies, and cloud services.
- Available in nano, USB-A and USB-C form factors.
Best for
Any organisation running its own PKI or signing infrastructure, where a private key sitting on a server filesystem is the weakest link.
Typical uses
Certificate authority root and issuing key protection, code and firmware signing, database and file encryption keys, Microsoft Entra ID certificates, IoT gateway trust.