YubiHSM 2 FIPS
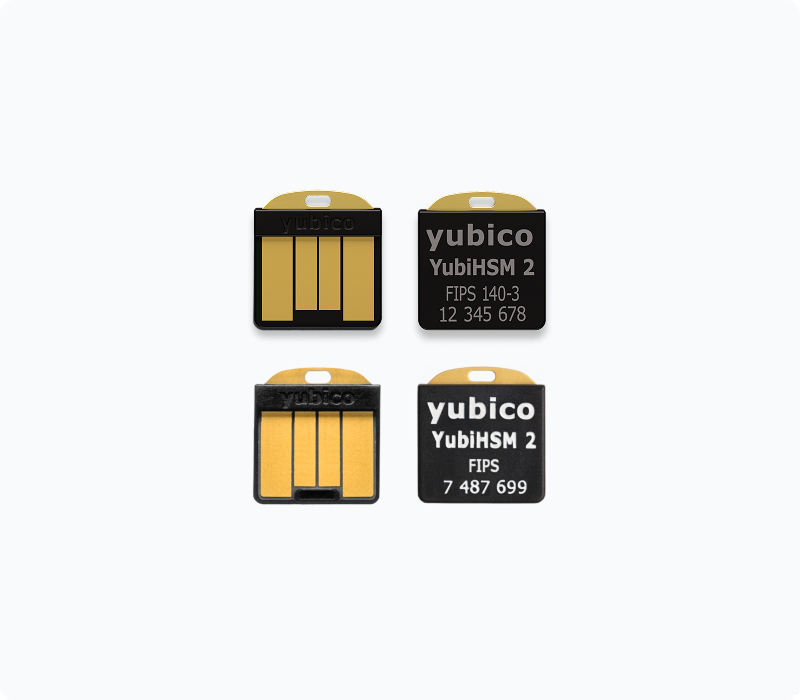
The YubiHSM 2, FIPS 140-3 validated, for PKI that has to satisfy an auditor.
Not a traditional HSM
A nano-format HSM, FIPS 140-3 validated, protecting infrastructure for which a rack-mounted appliance would be disproportionate.
Enhanced protection for cryptographic keys
Secure generation, storage and management of digital keys, performed in hardware.
Rapid integration with hardware-backed security
A comprehensive open-source cryptographic toolbox, with support for PKCS#11.
Simplified deployment for organisations of all sizes
An ultra-portable form factor at a price that suits both long-standing and emerging use cases.
Overview
The same device and the same integration path as the YubiHSM 2, validated to FIPS 140-3. Where a certificate authority underpins regulated services, auditors and procurement frameworks frequently require the key-protection hardware itself to be validated rather than merely equivalent. This is the variant that answers that requirement.
Specifications
- Protocols
-
- PKCS#11
- YubiHSM KSP (Windows)
- Native libraries
- Direct USB
- Form factors
-
- Nano
- USB-A
- USB-C
- Certification
- FIPS 140-3 validated.
- Durability
- IP68 rated, crush resistant, no batteries, no moving parts
Key protection
- Private keys are generated and held in hardware, so they cannot be copied off the machine or redistributed.
- Remote extraction of a private key is eliminated: signing and decryption happen on the device, and the key never leaves it.
- The YubiHSM 2's own authentication key can itself be stored on a YubiKey, removing one more password from the process.
- Backups use asymmetric wrapping, so a wrapped export exposes no secrets even when it crosses a network to another site.
Integration
- An open-source SDK, so integration work is not gated behind a vendor engagement.
- Exposed through PKCS#11, the industry standard interface, so most existing software can use it without modification.
- Hardware-backed key storage can be built into your own platforms, applications and services.
Deployment
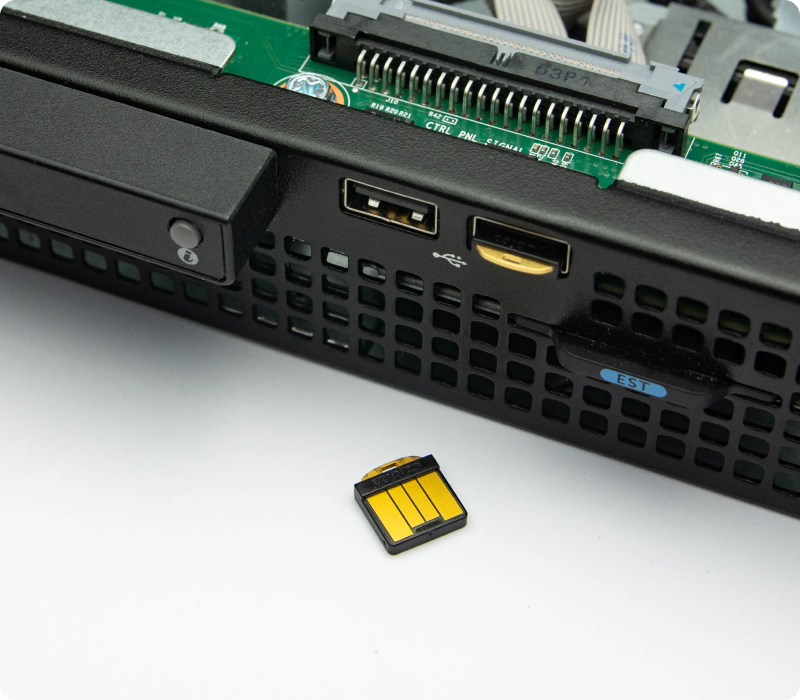
- Fits a front USB slot on a server or workstation — no rack space, no power, no cabling.
- Protects Microsoft Entra ID certificates.
- Used to secure cryptocurrency exchanges, IoT gateways and proxies, and cloud services.
- Available in nano, USB-A and USB-C form factors.
Best for
Regulated PKI — financial services, government, and critical infrastructure — where the HSM protecting the root must itself carry validation.
Typical uses
FIPS-validated certificate authority, regulated code signing, compliance-driven key management.